Cyber Liability Insurance Rules: Qualification Standards, Deductibles, and Policy Exclusions
A detailed guide for small and medium-sized businesses on commercial cyber policy coverage, mandatory security controls, ransomware sub-limits, and common grounds for claim denials.
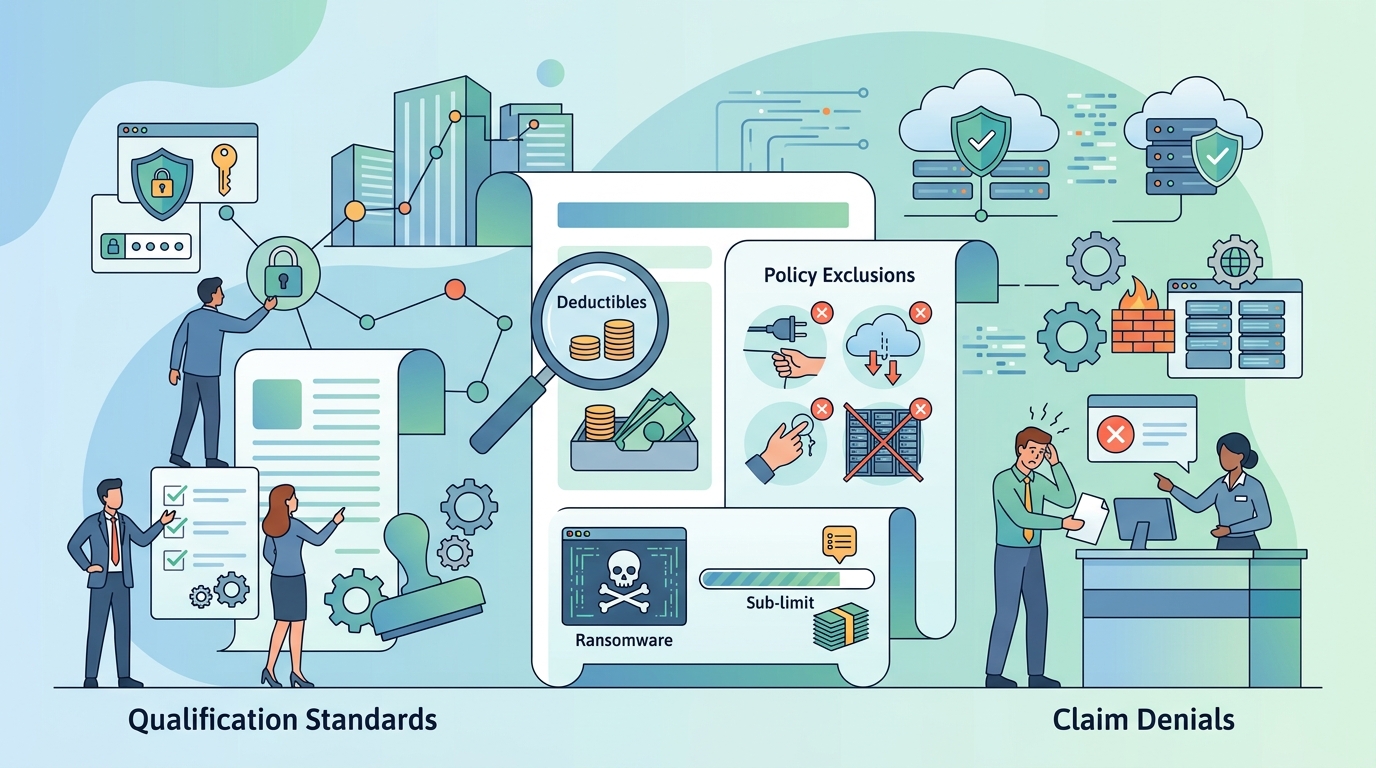
Understanding Commercial Cyber Liability Coverage
Small and medium-sized businesses rely heavily on digital infrastructure to store sensitive records, process payments, and manage daily operations. As cyber threats increase, commercial risk management requires a clear understanding of specialized insurance policies (Source 1). Cyber liability insurance protects organizations from the financial fallout of data breaches, ransomware attacks, and system outages. However, coverage is not uniform across all policies.
Commercial cyber policies are broadly divided into two major categories: first-party coverage and third-party coverage. First-party coverage addresses direct financial losses suffered by your business as a result of a security incident. This includes the immediate costs required to secure systems, investigate the source of an intrusion, and restore operational capacity. Guidance from regulatory bodies emphasizes that early technical remediation and investigation are essential for mitigating damage following a breach (Source 1).
Third-party coverage protects your business when external parties, such as customers, vendors, or regulatory agencies, hold you accountable for a security failure. If compromised systems lead to the exposure of confidential customer data, third-party coverage responds to lawsuits, legal defense fees, settlements, and potential administrative fines where permitted by law.
| Coverage Category | Primary Scope | Typical Included Expenses |
|---|---|---|
| First-Party Coverage | Direct operational losses incurred by the insured entity | IT forensics, data restoration, extortion negotiation, crisis PR, business interruption loss |
| Third-Party Coverage | Liabilities owed to external entities affected by a breach | Legal defense fees, civil litigation settlements, regulatory defense, consumer notifications |
Mandatory Cyber Security Insurance Requirements for Underwriting
In response to rising claim volumes, insurance carriers have established strict cyber security insurance requirements. In the past, companies could secure coverage by completing basic questionnaires. Today, underwriters demand proof that technical safeguards are actively operational before approving a application.
Securing coverage requires organizations to demonstrate baseline technical controls across all digital entry points (Source 1). Insurers assess technical posture through automated network scans and verified questionnaires. Organizations that fail to meet minimum underwriting requirements face application rejections, higher premiums, or restrictive coverage exclusions.
- Endpoint Detection and Response (EDR): Continuous monitoring tools deployed across all workstations and servers to detect and isolate malicious activity.
- Immutable Backup Isolation: Backup architectures that maintain air-gapped or immutable copies of critical data, preventing ransomware from corrupting historical recovery points.
- Patch Management Policy: Formal processes ensuring software updates and critical security patches are installed within designated timeframes.
- Privileged Access Management (PAM): Strict controls restricting administrative credentials to authorized personnel using the principle of least privilege.
Backup isolation is a primary focal point during underwriting. If an organization maintains continuous online network connectivity to its backup repositories, ransomware can encrypt both primary operational data and secondary backups simultaneously. Federal trade guidelines highlight that offsite or logically separated backups are essential for business resilience (Source 1).
Multi-Factor Authentication Insurance Qualification Standards
Among all technical safeguards, multi-factor authentication insurance qualification represents the single most important requirement for obtaining policy approval. Multi-factor authentication (MFA) requires users to provide two or more verification factors to gain access to digital resources (Source 1).
Insurers require multi-factor authentication implementation across three critical operational areas:
- Remote Network Access: Mandatory MFA for all Virtual Private Network (VPN) logins, Remote Desktop Protocol (RDP) sessions, and remote access software.
- Email Infrastructure: Enforced MFA for all employee webmail logins and cloud platform management access.
- Administrative Access: Verification protocols required for any user accessing cloud console settings, directory services, or core infrastructure.
Partial MFA implementation is frequently treated by underwriters as no implementation at all. For example, if an organization deploys MFA for email access but exempts remote contractors accessing the internal network via VPN, an insurer may deny coverage or issue a specialized endorsement limiting payouts in the event of an entry point breach.
Ransomware Coverage Exclusions, Sub-Limits, and Deductibles
Ransomware remains one of the most severe risks for commercial network environments. Consequently, insurers have introduced ransomware coverage exclusions, sub-limits, and co-insurance structures to limit their total payout exposure.
Commercial cyber policy limits might state an overall policy limit of $1,000,000, but contain a specific ransomware sub-limit capped at $250,000. Under this structure, the carrier will pay no more than the sub-limit for extortion demands, ransom negotiations, and specialized forensic decryption, even if total recovery costs exceed the baseline limit.
| Policy Structure Element | Operational Mechanism | Impact on Business Recovery |
|---|---|---|
| Extortion Sub-Limit | Caps total payouts specifically for ransom payments and negotiation fees | Forces policyholders to pay extortion demands exceeding the specific sub-limit out of pocket |
| Coinsurance Provision | Requires policyholder to share a percentage of total losses (e.g., 20%) | Increases out-of-pocket costs directly alongside total claim size |
| Waiting Period Deductible | Establishes a mandatory hour threshold (e.g., 8–24 hours) before business interruption coverage begins | Eliminates reimbursement for short-duration system downtime |
Deductibles in cyber policies can operate as flat dollar amounts or time-based thresholds. Dollar deductibles apply to direct financial expenses, such as hiring forensic accountants or rebuilding corrupted databases. In contrast, waiting period deductibles apply specifically to business interruption claims, requiring the business to absorb all downtime losses during the initial hours of an outage.
Critical Policy Exclusions: War Clauses, Unpatched Software, and Wire Fraud
Understanding common policy exclusions is vital for avoiding unexpected claim denials after an incident. Insurers evaluate claims against standard policy exclusions to determine whether an attack falls within covered terms.
State-sponsored cyberattacks represent a major legal issue regarding policy exclusions. Traditional insurance policies contain war and hostilities exclusions. When government agencies attribute an advanced persistent threat (APT) to a foreign state actor, carriers may invoke war exclusions to deny coverage. Modern policy amendments often require explicit language clarifying whether state-backed cyber espionage or digital warfare is covered.
Unpatched software exclusions present another common challenge for policyholders. Insurers frequently reject claims if an investigation reveals that the entry point of the breach was a known system vulnerability for which a software patch was made available by the vendor but not installed within a reasonable timeframe (e.g., 30 to 60 days). Routine patch management is recommended by security agencies to maintain operational integrity (Source 1).
Social engineering and wire fraud schemes (such as Business Email Compromise) are frequently excluded from core cyber liability policies. If an employee is tricked into voluntarily transferring funds to a fraudulent bank account, the insurer may classify the event as crime or social engineering loss rather than a system intrusion. Securing protection for wire fraud typically requires adding a specific endorsement to the core policy.
Data Breach Notification Compliance Costs and Legal Expenses
When a security incident exposes sensitive personal data, businesses face strict regulatory notification requirements. Government guidelines mandate that businesses take prompt steps to notify affected parties and regulatory authorities following unauthorized data access (Source 1).
Compliance expenses accrue rapidly during breach response operations. Cyber liability insurance policies cover specific notification-related cost categories:
- Legal Consultation: Retaining specialized privacy counsel to interpret state, federal, and international notification mandates.
- Consumer Notification Distribution: Printing, mailing, or electronically distributing breach notification letters to affected individuals.
- Credit and Identity Monitoring Services: Providing mandated credit monitoring and identity theft restoration services to affected consumers (typically for 12 to 24 months).
- Call Center Operations: Establishing dedicated call centers to manage incoming inquiries from impacted clients or employees.
- Public Relations Retainers: Engaging specialized crisis communication firms to minimize reputational damage during public disclosure.
Cyber Liability Insurance Costs and Policy Premium Drivers
Cyber liability insurance costs vary across organizations based on risk exposure and underlying technical controls. Insurers calculate premiums by analyzing operational and organizational risk factors.
| Underwriting Factor | Risk Impact Description | Mitigation Strategy |
|---|---|---|
| Industry Sector | High-risk sectors (healthcare, finance) handle high volumes of sensitive data | Implement robust data segmentation and tokenization protocols |
| Annual Revenue | Larger operational scales present higher business interruption loss potential | Maintain clear continuity plans and secondary infrastructure redundancy |
| Record Volume | Storing higher volumes of personal information increases breach notification costs | Enforce strict data retention and purging schedules (Source 1) |
| Technical Controls | Absence of MFA or EDR results in sub-limits or higher pricing | Deploy unified authentication and endpoint monitoring tools |
Premium benchmarks published by industry rating bureaus show that implementing security measures—such as universal multi-factor authentication, endpoint monitoring, and verified offline backups—can lead to lower annual premiums compared to organizations without these technical safeguards.
Step-by-Step Security Protocol Checklist for Cyber Insurance Approval
To prepare for underwriting assessments and streamline policy renewal, organizations should complete a thorough security assessment. Ensuring all systems comply with core standards reduces the risk of coverage denials.
- Enforce Multi-Factor Authentication: Ensure MFA covers all remote access points, cloud services, and privileged admin accounts (Source 1).
- Establish Isolated Backups: Maintain offline, air-gapped, or immutable backup systems and conduct regular data restoration tests (Source 1).
- Implement Automated Patching: Configure system policies to install security patches promptly upon release.
- Conduct Employee Training: Perform routine phishing simulations and security awareness training for all active staff members (Source 1).
- Secure Vendor Connections: Restrict third-party vendor network access to dedicated, monitored connections with enforced session limits.
- Review Social Engineering Riders: Verify whether the existing policy includes explicit coverage for wire fraud and funds transfer losses.
What happens if a business inaccurate information on a cyber insurance application?
If a carrier discovers that an applicant provided inaccurate information regarding security controls—such as falsely claiming complete MFA deployment—the insurer may void the policy or deny claims arising from that misrepresentation.
Does standard commercial general liability insurance cover data breach losses?
Standard commercial general liability (CGL) policies typically exclude loss of electronic data and third-party privacy liabilities, making a dedicated cyber liability policy necessary for coverage.
How does a waiting period deductible function during a network outage?
A waiting period deductible requires the policyholder to absorb all financial losses sustained during a specified initial window of downtime (such as 8 or 12 hours) before insurance reimbursement for business interruption begins.
Sources
- Cybersecurity for Small Business — Federal Trade Commission
This article is for general information only and is not professional advice. Figures come from public sources and change over time; check the official source before you act.
More from True Money Net
- Save Up to 50 Percent on Dental Implants at Local Schools
- See 5 Essential Rules to Qualify for Free Implants
- Find 5 Official Low Cost Dental Programs for Seniors Today
- 5 Hidden Rules to Get Dental Implants Covered by Insurance
- SSDI Spousal Benefits: Eligibility Rules, Payment Limits, and Calculations
- FHA 203(k) Home Rehabilitation Loans: Appraisal Guidelines, Eligible Upgrades, and Fee Structures